
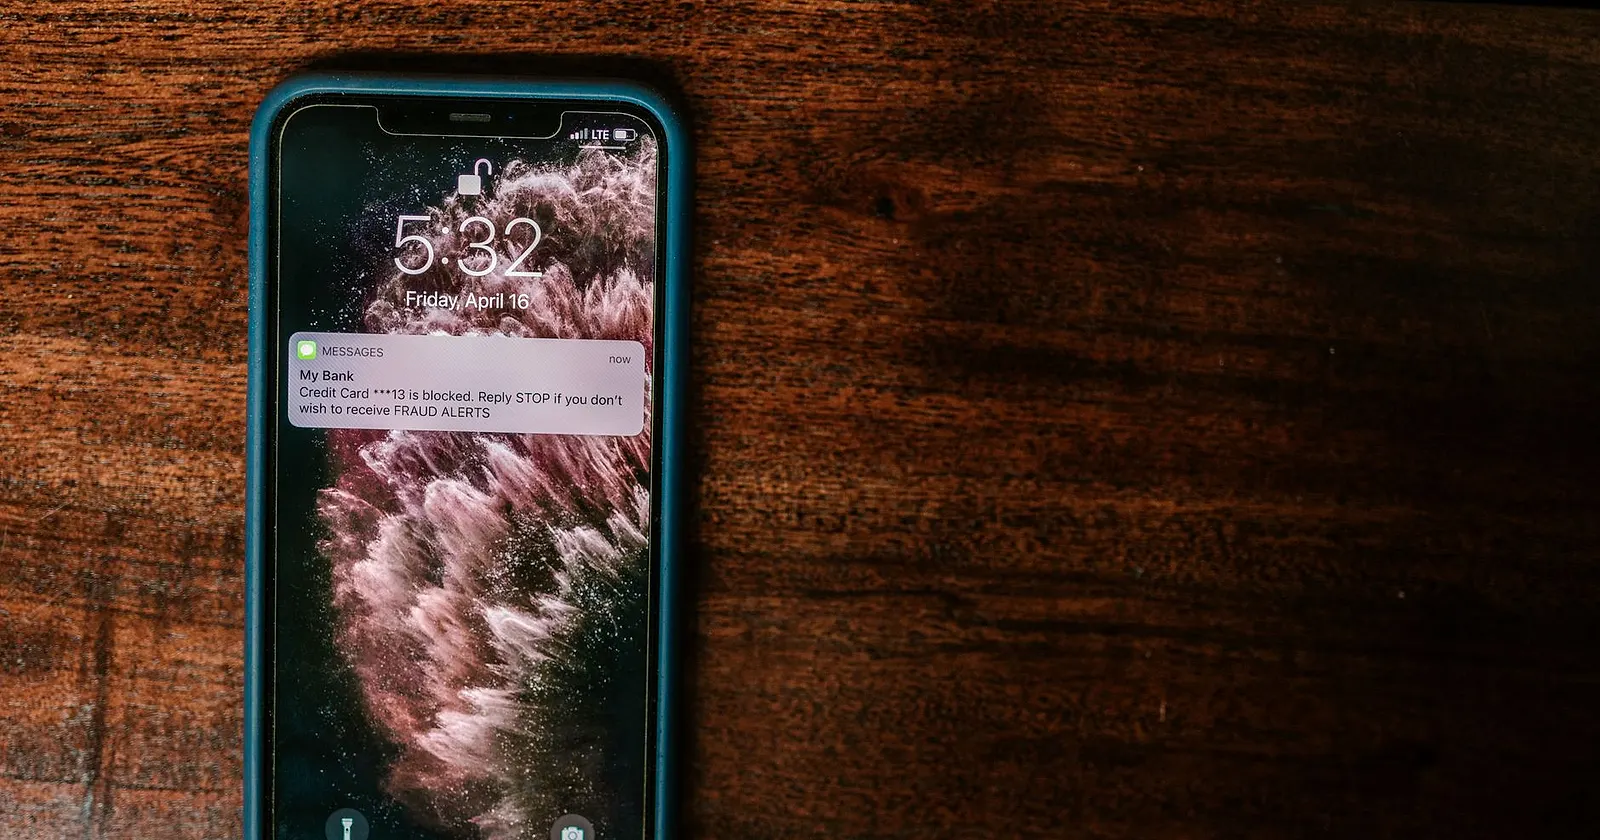
For most of the last decade, authorised payment fraud in Europe has been treated as the customer's problem. If you were tricked into sending the money yourself, the bank's liability was limited. The provisional agreement reached on 27 November 2025 on the Payment Services Regulation (PSR) and the third Payment Services Directive (PSD3) changes that assumption[1].
What was agreed
The package still needs formal adoption, but its direction is clear:
- Impersonation fraud refunds. Where a scammer pretends to be a bank employee and the customer approves the payment, the bank must refund the full amount, provided the customer reports it to the police and informs the bank.
- Fraudster-initiated payments. If a fraudster initiates or changes a transaction, it is treated as unauthorised and the bank is liable for the full amount.
- Payee name checks. Banks must check that a payee's name matches the account identifier and refuse the payment if it does not, telling the payer.
- Platform liability. Online platforms become liable to banks that have refunded customers if the platform was told about fraudulent content and failed to remove it.
- Advertising controls. Anyone advertising financial services on platforms must show they are authorised, or acting for someone who is.
- Customer controls. Banks must offer spending limits and blocking tools, and open banking users get a dashboard to see and manage the data permissions they have given.
Fraud moves onto the P&L
The practical effect is simple: a category of loss that sat with customers now sits with banks. That changes the economics of prevention. When losses were the customer's, fraud controls were justified mainly by regulation and reputation. When losses are the bank's, every avoided scam is money saved, and investment in behavioural analytics, real-time payment scoring and customer friction at the right moment has a direct, measurable return.
When fraud losses move onto the balance sheet, fraud prevention stops being a compliance cost and becomes a margin decision.
It also changes who inside the bank owns the problem. Fraud strategy will need a finance partner, a loss forecast and a budget that responds to it, in the way credit risk has always had.
The platform clause is only as good as your evidence
The most novel element is liability for platforms. Many impersonation and investment scams begin on social media, marketplaces or messaging services, long before the customer opens their banking app. For the first time, a bank that refunds a customer has a route to recover from a platform that ignored a warning.
But the right is conditional: the platform must have been informed and failed to act. Banks will only recover if they can prove notification, timing and the link between the content and the loss. That requires a capability most banks do not have today: a structured process for reporting fraudulent content to platforms, logging responses and tying them to specific cases.
What I would do in the next two quarters
- Re-baseline fraud losses assuming full refund of impersonation cases, and use it to reset the prevention budget.
- Build the platform evidence trail: standard notices, case references and response tracking, so that claims are possible when the rules apply.
- Treat name checks as a customer experience project. Mismatch messages that are clear and calm will stop fraud; confusing ones will train customers to click through.
- Ship spending limits and permission dashboards as features. They are required, but they are also visible proof that the bank is on the customer's side.
The final texts and application dates are still to come. The direction is not in doubt, and the banks that start now will set their loss rates rather than discover them.